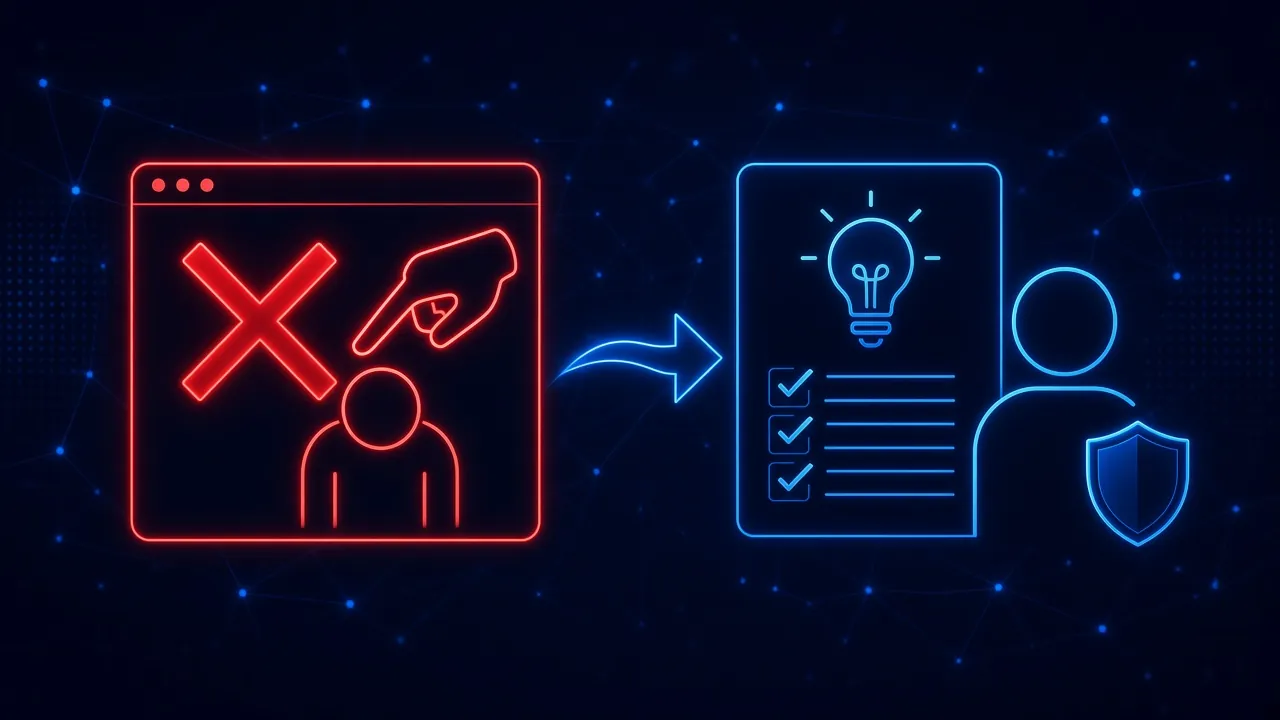
Cybersecurity is as much a complex psychological problem as it is a technological one, yet most cybersecurity training treats it like a simple test that employees will either pass or fail.
"One of the biggest flaws in cybersecurity training today is its pass/fail mentality."
The industry has long encouraged a culture of shame-based learning, where employees are penalized for mistakes but rarely recognized for success and where phishing tests and security drills are framed as traps rather than opportunities to learn, reinforcing the stigma that cybersecurity awareness is just "common sense." But if these threats were truly common sense, then low-tech attacks like phishing, business email compromise, and pretexting wouldn't be the most successful entry points for attackers. The solution lies in how cybersecurity education is structured, and how its failures play directly into the hands of attackers.
One of the biggest flaws in cybersecurity training today is its pass/fail mentality. When an employee fails a simulated phishing test, they are often singled out, prescribed extra training, and made to feel like a liability. This approach focuses on punishment rather than education, creating a culture of fear rather than empowerment, and it makes employees feel stupid, which is rarely a good motivator. Employees are therefore conditioned to hide mistakes rather than learn from them, and those who perform well receive no positive reinforcement at all. If failing a test results in embarrassment and additional work, but passing those tests goes unnoticed, then cybersecurity becomes something to dread rather than engage with. This system does not improve security awareness. It just makes employees hesitant, disempowered and resentful.
Research has shown that shame-based learning is one of the least effective ways to change behavior. Studies in psychology and education confirm that learning is best reinforced through positive feedback, engagement, and a sense of achievement rather than punishment. According to Dr. Brené Brown, a leading researcher on shame and learning, "shame corrodes the very part of us that believes we are capable of change." In cybersecurity training, this means that if employees feel ashamed of their mistakes, they are less likely to engage with training and more likely to dismiss it altogether. Studies in workplace education also suggest that intrinsic motivation (feeling like you are learning something valuable) is far more effective than extrinsic motivation, like avoiding punishment. If cybersecurity training fails to engage employees as active participants, it fails entirely.
"Attackers rely on this culture of shame to keep their tactics effective.."
The irony is that attackers rely on this culture of shame to keep their tactics effective. Phishing, social engineering, and other "low-tech" cyberattacks continue to work because employees hesitate to report suspicious activity for fear of looking foolish. This hesitation is exactly what attackers count on. If organizations remove the stigma around cybersecurity mistakes and instead reward engagement, curiosity, and progress, employees would feel empowered rather than embarrassed to ask questions, verify suspicious messages, and actively participate in their company's security.
"By removing the negative stigma around failure and instead celebrating progress, organizations can make cybersecurity a habit rather than a hurdle"
Cybersecurity training needs a paradigm shift that moves away from punishment and toward recognition, engagement, and continuous learning. Security awareness should feel like a skill employees take pride in, not a mandatory compliance exercise that tests your most basic intelligence. By removing the negative stigma around failure and instead celebrating progress, organizations can make cybersecurity a habit rather than a hurdle, one that attackers will find much harder to exploit. That is the philosophy behind SavvyShield's approach to security awareness training: contextual, positive, and continuous.